Digital Governance Strategy Presented to Turkeys Cyber Security Council
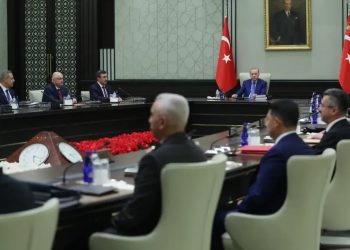
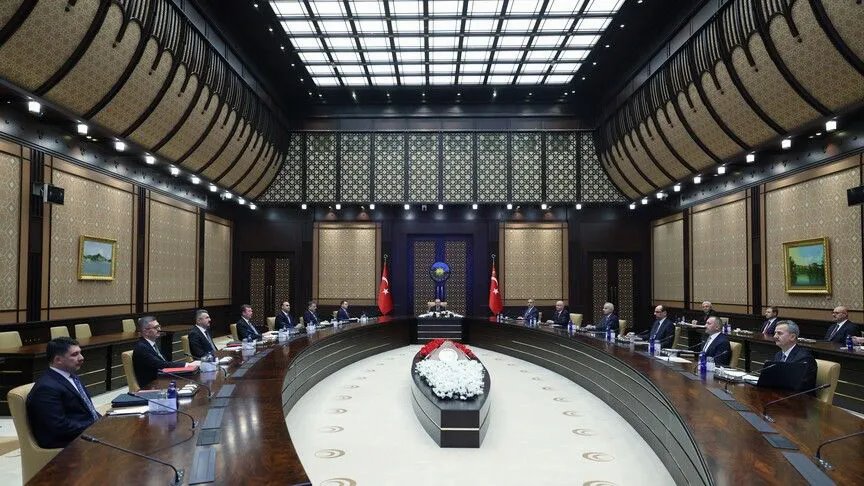
According to the Communications Directorate of the Presidency of Turkey, the meeting of the country’s Cyber Security Council was held under the chairmanship of Recep Tayyip Erdogan. At the meeting, the Digital Governance Strategy was presented with the aim of strengthening Turkey’s sovereignty in the digital space, reducing dependence on foreign countries in the field of critical technologies, and developing national technology capacities.
The Communications Directorate of the Presidency of Turkey stated: “The Digital Governance Strategy, prepared with the aim of strengthening Turkey’s sovereignty in the digital space, reducing dependence on foreign countries in the field of critical technologies, and developing national technology capacities, was presented to the Cyber Security Council.”
At the meeting, the impact of global and regional geopolitical developments on the cyber security environment, current events in the international arena, and changes in threat dynamics were comprehensively reviewed. The impact of advances in artificial intelligence on the nature, scope, and speed of cyber threats was also explained, and the consequences and risks of algorithmic manipulation and cognitive influence activities through digital platforms for national security and social resilience were evaluated.
In the final statement of the meeting, the importance of digital governance for national security was emphasized. The protection of critical infrastructure, strengthening national cyber resilience and deterrence capacity, and achieving technological independence were also declared among Turkey’s strategic priorities in the fields of security and development.
According to the statement, relevant institutions and organizations were instructed to implement the decisions taken in line with the strategic objectives of the Digital Governance Strategy within the framework of their duties and responsibilities. Effective monitoring of the implementation process and regular evaluation of progress were also emphasized.
Considering the rapid spread of cyber threats and their capacity to affect different sectors simultaneously, emphasis was placed on strengthening coordination and cooperation among institutions, developing joint risk assessment capacities, and establishing integrated procedures in implementation. The commitment to expanding cooperation among public institutions, the private sector, and universities and to developing a comprehensive cyber security ecosystem was once again reaffirmed.